

User-Controlled Model Integrations
Users integrate their own API keys and select the model providers they want to work with. As a result:- Orq.ai does not require Data Processing Agreements (DPAs) with model providers nor is Orq.ai a subprocessor for the model providers.
- Whether a model trains on the data depends on settings configured on the provider’s side. Most providers allow training to be disabled; this must be configured directly in the provider’s platform by the user.
No Model Training on Platform Data
No data that flows through Orq.ai is ever used to train or fine-tune any models by Orq.ai. Input and output data in traces, logs, threads, and responses are processed for observability and evaluation purposes and retained only for the configured retention period.Privacy and Masking Controls
Orq.ai includes features to help ensure data privacy and regulatory compliance:Input Masking
Input variables can be flagged as Personally Identifiable Information (PII), which includes Personal Data. These are sent to the model but are not stored or shown in logs.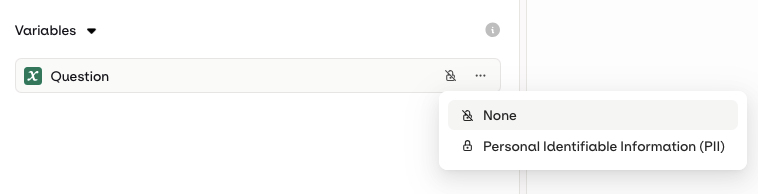
Flag an input as PII in the Security tab of your variant. Once deployed, the value is sent to the model but never stored.
Output Masking
Entire model responses can be masked. While tokens are still exchanged with the model, the content is never stored or displayed within Orq.ai.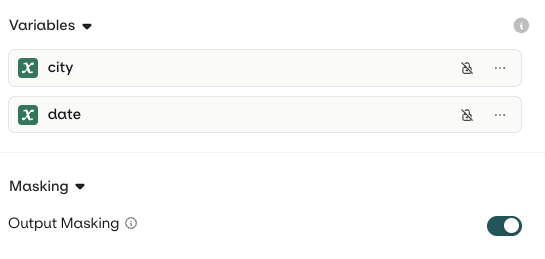
Enable Output Masking to prevent generated responses from being stored in logs and traces.
Security and Compliance
- Compliance is maintained through Vanta, supporting both SOC 2 Type 2 and GDPR standards. Audit reports and the current status are at trust.orq.ai.
- Security oversight is provided by an independent Chief Information Security Officer (CISO).
- All data stored within the Orq.ai-hosted platform resides in data centers located in the European Union.